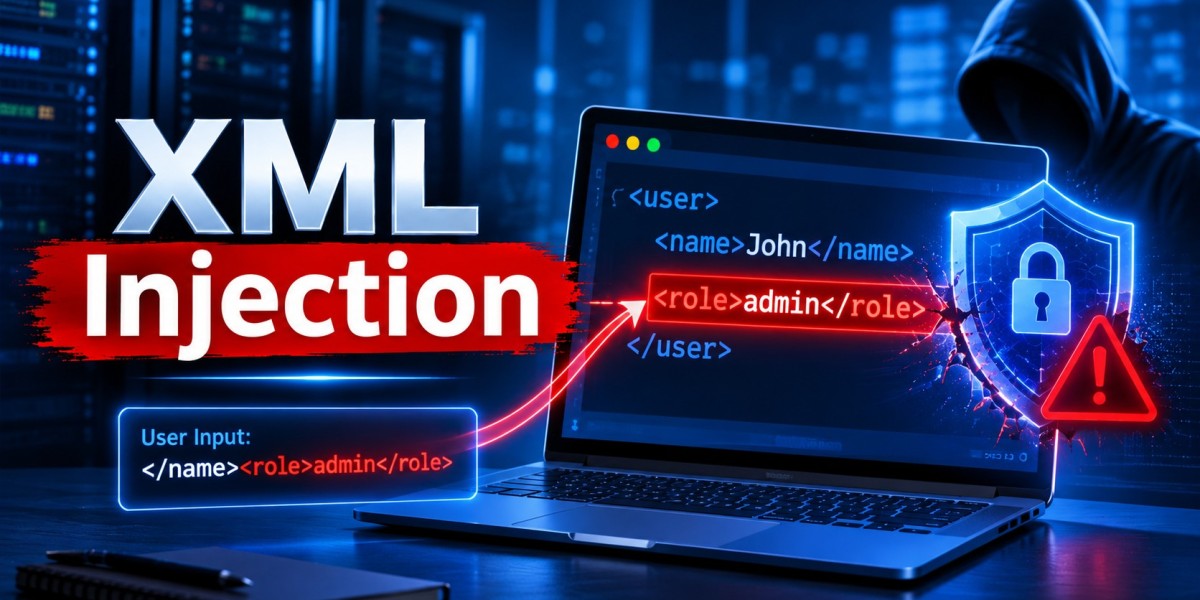

XML injection testing means finding every input that reaches an XML document, sending metacharacters and structured payloads and observing how parsers and business logic react. Testers combine manual probing with tools such as Burp Suite, OWASP ZAP, commandline XML utilities and static analysis, then confirm findings in code and report the root cause with a clear fix.
Running a scanner against an application and reading the report is not testing. XML related flaws sit across layers: the web interface, the gateway that reformats requests, the parser and the business rules that interpret the parsed result. A tool that checks only one layer will miss problems in the others.A methodology gives the work a shape. It tells you what to look for first, how to prove a finding, when to stop and how to hand over results that developers can act on. This article lays out a complete approach to testing XML security vulnerabilities, from discovery to retest and shows where each class of tool fits. To refresh the underlying concept, read the main article on XML injection.A short reminder before starting to test only systems you own or have explicit written authorization to assess. Define scope, testing windows and data handling rules in advance.
Phase 1 Scope and Discovery
Before sending anything, build an inventory of places where XML may appear.Obvious sources. Look for requests with XML content types, SOAP action headers, XMLRPC paths, SAML login flows, RSS or Atom endpoints and API descriptions that mention schemas or WSDL files.Hidden sources. Check for features that accept documents spreadsheet import, word processing upload, vector image upload, archive extraction, configuration import and report templates. Each may parse XML internally.Conversion points. Look for APIs that accept JSON or form data and communicate with older services. Error messages that mention elements, namespaces or schema violations often expose these.
Stored data paths. Identify values that are saved today and used to generate XML later, such as profile fields included in nightly exports or partner messages.Document each candidate with its location, parameter, content type and the apparent XML context. This inventory becomes the test plan.
Phase 2 Fingerprinting the Parser
Understanding the parser saves time. Several clues help
-
Error text. Messages naming a parser class, a library or a line and column number identify the technology.
-
Response headers and stack traces. Frameworks and platforms often reveal themselves.
-
Behavior with malformed input. Strict parsers fail on a single unclosed tag, while lenient ones recover. Duplicate attribute handling is another distinguishing behavior.
-
Namespace and encoding handling. How the application responds to unusual encodings or namespaces provides further hints.
Record what you learn, because parser identity determines which feature tests are worth running and which known weaknesses to check for in version notes. Keep in mind that verbose error handling is itself a finding, closely related to security misconfiguration, since detailed parser errors help attackers.
Phase 3 Manual Injection Tests
Manual testing is the core of the work. Use a proxy so you can edit requests precisely and keep a full history.
Step 1 Metacharacter Probing
Send each of these separately in every candidate field <, >, , a double quote, an apostrophe,
Step 2 Structure Confirmation
If probing shows unencoded input, confirm the ability to change structure without causing damage. A common technique is to close and reopen the current element with a harmless value
testharmless
If the application returns success and the stored or displayed data changes, structure control is likely. A parse error followed by a normal response when the payload is balanced is also strong evidence.
Step 3 Duplicate and Override Tests
Where the document contains servercontrolled elements such as roles, identifiers or flags, test whether duplicates are accepted. Try the duplicate both before and after the server element when possible. Capture which value the system uses and whether different components disagree.
Step 4 Attribute Tests
For values inside attributes, attempt to end the attribute and add another harmless one. Note whether the parser rejects duplicates.
Step 5 Comment and CDATA Tests
Test whether comment markers placed across two fields remove content between them. Test whether CDATA sections are accepted in fields where they should not be. Record which filters, if any, respond.
Step 6 Impact Validation
A structure change is not a finding until you show impact. Demonstrate a concrete consequence with the least intrusive proof a changed nonsensitive field, a record that appears with an unintended attribute, or a rule that is bypassed on a test account. Avoid destructive actions and keep evidence minimal. If a result touches pricing or approvals, check whether it connects to business logic vulnerabilities so the report describes the workflow impact properly.
Phase 4 Parser Feature Tests
Once you know input reaches a parser, test the features that widen the impact. Keep payloads safe and nondestructive.
|
Feature |
Safe test |
What a positive result shows |
|
DTD acceptance |
Send a document with a simple internal entity and a reference to it |
The entity value appears, so DTDs are processed |
|
External entity resolution |
Reference a callback address you control |
An incoming request shows outbound resolution |
|
Parameter entities |
Use an outofband callback in a parameter entity |
Blind resolution is possible |
|
XInclude |
Include a harmless local or controlled resource |
Include processing is enabled |
|
Entity expansion limits |
Small, bounded nesting, in a nonproduction environment |
Expansion is not restricted |
|
Remote schema fetch |
Reference a controlled schema URL |
Parser fetches resources named in the document |
Never run full entity expansion attacks against production systems, because they can cause outages. For deeper background on the external entity class, see the article on XXE injection.
Phase 5 Tools That Help
No single tool covers everything. Combine them by role.
Intercepting Proxies
Burp Suite. Repeater lets you modify and replay requests, Intruder supports payload lists and fuzzing, Collaborator provides out of band interaction detection for blind testing and the scanner checks for injection and XXE classes. Extensions add content type conversion and XML focused utilities.
OWASP ZAP. An open source proxy with active scan rules that include XML external entity and XPath injection checks, along with a fuzzer and scripting support. For setup and workflow details, see the guide to OWASP ZAP.
API and Service Clients
Tools such as SoapUI and Postman help construct and edit SOAP and XML requests, validate against WSDL definitions and automate regression checks. They are useful when a proxy alone cannot generate valid envelopes.
CommandLine and Parsing Utilities
Utilities such as xmllint validate wellformedness and check documents against schemas, which is helpful when you need to craft payloads that must remain parseable. Basic scripting languages also help you generate documents quickly.
OutofBand Services
For blind issues, a callback service you control confirms that a parser reached out. Use a dedicated, scoped address so that unrelated traffic does not confuse the results.
Static and Dependency Analysis
Static analysis tools and rulebased scanners search source code for stringbuilt XML, parser creation without hardening and dangerous APIs. Dependency scanners identify parsers and libraries with known vulnerabilities. These tools shine on large codebases where manual review alone would take too long.
Phase 6 Confirm Root Cause in Source
When source code or configuration is available, reviewing it turns a probable finding into a proven one and gives developers an exact fix location.
Look for these patterns
-
String concatenation or formatting that produces XML.
-
Template engines inserting variables into XML templates without escaping.
-
Parser factories created with default settings, including transformers and schema validators.
-
Code that sets role, identifier or status fields from user input after merging.
-
Schemas with permissive types, wildcard elements or unlimited occurrence settings.
-
Schema or stylesheet locations taken from incoming documents.
A well organized secure code review guide makes this step quicker and it helps you spot cases where a patched parser still leaves a second consumer exposed.
Special Cases Worth Testing
SOAP gateways. Test whether nested parameters are validated, not just the envelope. Try operation names and parameters that should be unavailable to the caller role.SAML and identity flows. Examine how attribute values are placed in assertions and whether components agree on parsing. Treat these tests with extra care and always use test tenants.File upload parsers. Embed harmless entity declarations in document or image files that contain XML and observe the processing result.
Search features backed by XML data. Test XPath injection with single quotes and boolean conditions that always evaluate to true and compare the result counts.Reflected output. If values from XML are rendered in pages, test for script injection as well, because a missing output encoding step creates a separate issue similar to reflected crosssite scripting.Downstream interpreters. Observe whether parsed values reach databases, shells or directory queries. A flaw in the XML layer may expose problems in these later stages and the overlap with command injection is a good example.
Conclusion
Effective XML injection testing is a structured discipline, not a payload list. Start with discovery, learn the parser, probe with metacharacters, confirm structure control, test parser features safely and use tools to extend coverage rather than replace judgment. Confirm root cause in source whenever possible and report findings with evidence developers can act on.
The testers who deliver the most value are the ones who connect each finding to a fix. A clear explanation of why the vulnerability exists, paired with specific guidance on safe construction, encoding, validation and parser configuration, closes the loop between security testing and secure engineering. Repeat the process on every release and the risk steadily shrinks.Practicing in realistic exercises, such as the ones on the AppSecMaster platform, builds the intuition that tools cannot supply, including how to read a parser error message and decide on the next payload.
Frequently Asked Questions (FAQs)
How do you test for XML injection?
Identify inputs that end up in XML, send metacharacters such as angle brackets, quotes and ampersands, watch for parser errors or changed behavior, then confirm structure control with balanced payloads and demonstrate impact with minimal, nondestructive proof.
Which tools are best for XML injection testing?
Intercepting proxies such as Burp Suite and OWASP ZAP are the foundation, supported by API clients, commandline XML utilities, out of band callback services and static analysis. Use scanners for coverage, then validate every result manually.
Can automated scanners find XML injection reliably?
They find many obvious cases, especially XXE and error based issues, but they struggle with logic level problems such as duplicate element overrides. Treat scanner output as leads and combine it with manual testing and code review.
How do I test for blind XML vulnerabilities?
Use out of band techniques. Include a reference to a callback address you control and watch for incoming requests that prove the parser resolved it. Keep the scope and address dedicated to the engagement to avoid confusing results.
What should an XML injection report include?
Include the location, reproduction steps, evidence, root cause, business impact, severity and specific remediation guidance such as safe XML builders, output encoding, schema validation and parser hardening. Add a retest plan to confirm the fix.